
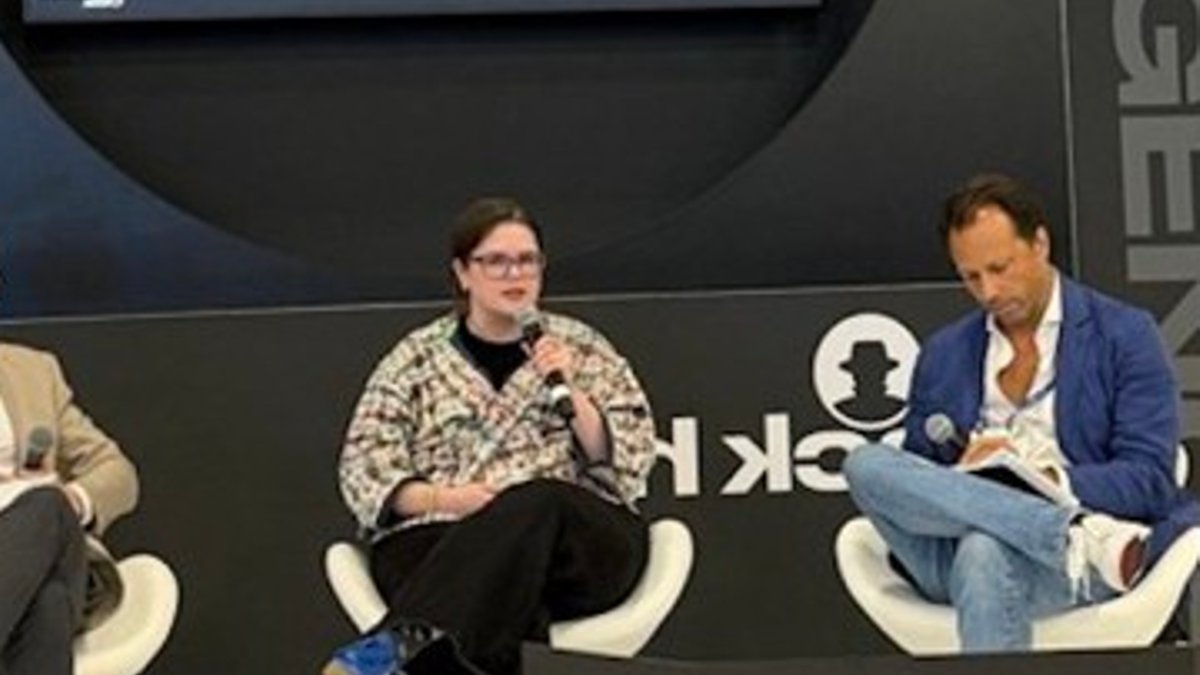
Lindsey Cerkovnik, the branch chief for vulnerability response and coordination at the Cybersecurity and Infrastructure Security Agency (CISA), is leaving the agency after nearly six years. She plans to start a new role in November.
Cerkovnik’s office helps oversee the Common Vulnerabilities and Exposures (CVE) Program, a key global system for tracking software vulnerabilities. Her departure comes amid global discussions over how to sustain this program.
The CVE Program assigns standardized identifiers to software flaws, allowing researchers, vendors, and governments to track the same problems. It is used by virtually all cyber practitioners, from software developers to analysts inside national intelligence agencies.
At an August panel during the Black Hat cybersecurity conference, Cerkovnik said the CVE program could keep up as researchers discover more software flaws. But the harder task, she said, would be helping organizations distinguish weaknesses that pose a serious threat from those that are less urgent to fix.
Cerkovnik joined CISA in May 2021 to lead vulnerability management for industrial control systems. She became branch chief in May 2023, after serving as acting chief of the agency’s vulnerability response and disclosure section.
Before CISA, Cerkovnik spent over four years at Idaho National Laboratory, working on control systems cybersecurity and cyber investigations. Her work has involved programs that help agencies and businesses identify security weaknesses and decide which need urgent repairs.
Cerkovnik’s departure comes as artificial intelligence-assisted vulnerability research puts new pressure on efforts to clamp down on digital security flaws. This week, CISA joined the NSA and FBI in urging organizations to fix critical flaws in PHP, widely used software that helps run websites worldwide.
Cerkovnik highlighted the agency’s response to Log4Shell, the launch of a coordinated vulnerability disclosure platform, and work on the Known Exploited Vulnerabilities catalog in her LinkedIn post. The catalog identifies flaws that hackers have already exploited, helping organizations prioritize fixes.


